I'm completing my degree in Software Engineering at the University of Seville, and I learn backend engineering and Application Security by shipping real projects: a phishing detector, a secret scanner, a local-first study tool and a honeypot lab. Every project starts from the same question: how does this work under pressure? And none is finished until it ships with tests and CI.
Security appeals to me because it forces two perspectives at once: the builder's and the attacker's. So I write software assuming someone will try to break it.
- English
- B2 Cambridge certified Preparing for Cambridge C1 Advanced
Refining Error Log C1 after its v2.0 release: a local-first Next.js app that turns Cambridge C1 practice mistakes into one concrete weekly action, with transactional batch import, SQLite backup and restore, indexed search and AnkiConnect review sync.
Projects I've built.
From Security+ to OSCP.
The plan: fundamentals first, then cloud, then offensive security. Alongside it, I keep building tools like the ones above.
After Security+: eJPT, then OSCP.
Stack, by project.
Also in my toolkit:
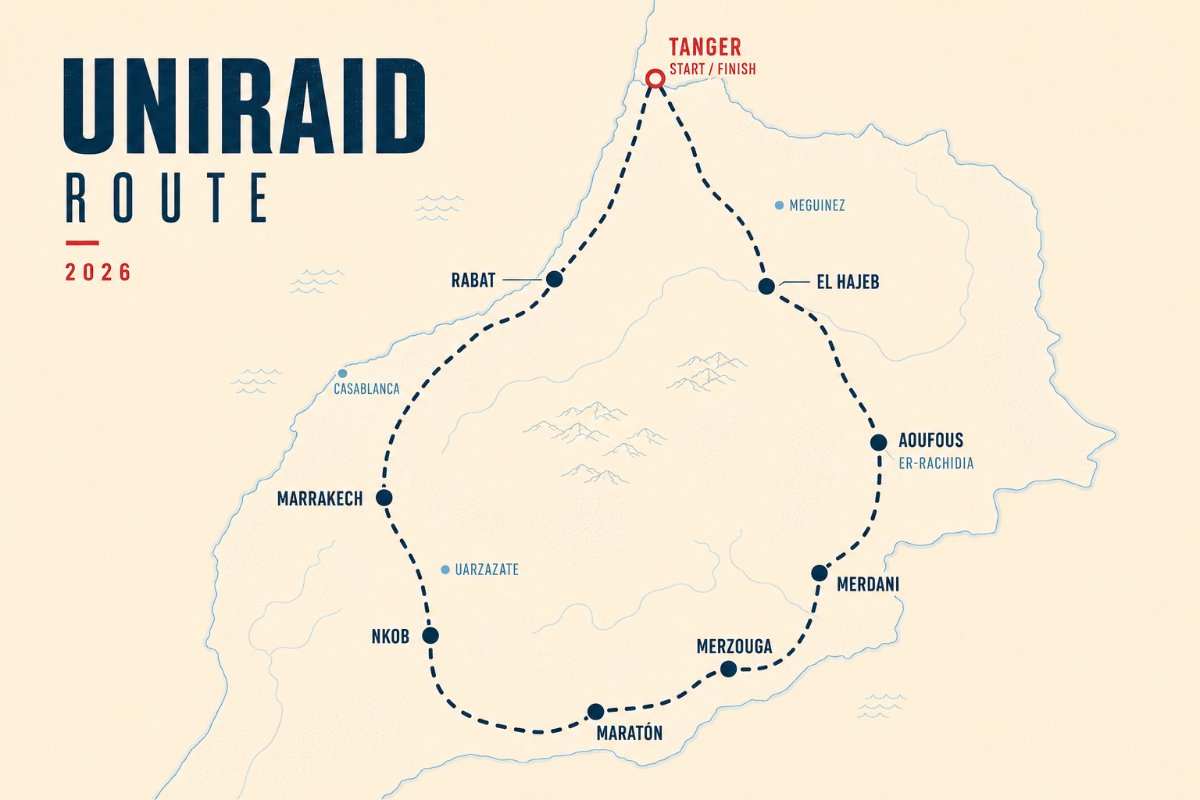
UniRaid.
I take part in UniRaid with Los Pata Negra, a team joining this student solidarity rally across Morocco in a classic car to deliver humanitarian aid to underserved communities.
Something to build or break?
I'm looking for internships in backend, Application Security or product engineering, and I'm open to collaborations and projects. The fastest way to reach me: